

Hacker, organizer, cheese eater. ½ Syrian, ½ Dutch.
Amsterdam
- Tweets 2,728
- Following 3,008
- Followers 2,937
- Likes 49,096


Prettymux had this for a while and fully open source github.com/patcito/prettymux

In the last 18 months or so my terminal use has exploded. From being a place where I mostly navigated the file system, ran a server and did some very light nvim use, to my entire workspace, connected to multiple machines, where I spend most of my day.
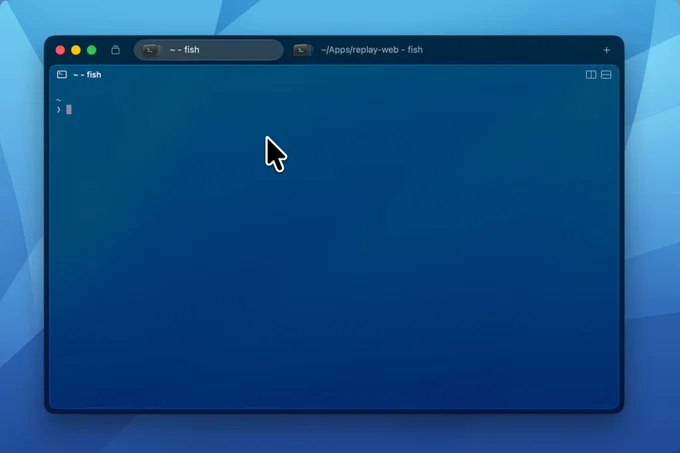
This is the starting point we're using for designing the @superlogical multiplexer, and we're borrowing ideas from another app that blurs the local and remote, long lived sessions and throwaway tabs: the web browser.
And the first thing I wanted to borrow: favicons, for your terminal apps.
We call it the Deck icon (like a deck of cards), since it needs to represent your own layout of (potentially) multiple running processes.
2
5
818
So sick of American models bs guardrails, I hope they go away with Kimi k3

I have a report full of security issues of a software I'm working on.
Codex won't fix them because of Cyber guardrails
Fable won't fix them because of Cyber guardrails
Kimi K3 fixed them all. No restrictions, just gets the job done.
This will end badly for OpenAI & Anthropic.
2
5
302

The safe.global and MetaMask teams (both incredibly skilled) share a unique talent: making their already terrible UX even worse with every release
2
2
144

Please ban competition to save democracy

We've published a paper that explains our views on AI competition between the US and China.
The US and democratic allies hold the lead in frontier AI today. Read more on what it’ll take to keep that lead: anthropic.com/research/2028-…
2
2
316


I love niri horizontal scrolling layout, it's also supported in omarchy btw.
Couldn't resist adding support for it in prettymux this weekend, been using it for a couple of days and it's really nice.
Added a bunch of fixes and features two, also received 5 PRs and a few stars already. Link below.

2
3
7
324
if you have prettymux installed, you can just update your package or get it here:
website prettymux.com/
repo: github.com/patcito/prettymux
1
109
Of course you can vibecode Morpho
Step 1: write a dummy solidity contact
Step 2: make sure it gets zero revenue
Step 3: ???
Step 4: 0 profit
Congrats, you've just written your own Morpho
It's a joke people, calm down

you can’t prompt engineer morpho for two reasons:
- each new version is a super small piece of code that takes months to build/secure and it usually comes after 1year+ of design
- building the network (liquidity) is an extremely intensive and multidimensional process: from a team flying all over the world, to apps, to trust building, etc
199

tl;dr USDC supply apy about to pump for a short while

A proposal on AAVE USDC market and liquidity parameters from Circle's Chief Economist @gordonliao
governance.aave.com/t/arfc-i…
1
278
Yep

It shocks me that most of CT is focused on the attack vector itself, LZ and rsETH's security model. As an @aave creditor, all my rage is on their curators for not assessing this risk correctly. This is their only task and this is where our trust in the protocol lies.
3
180
tbf, no one disagrees with freezing bad actors funds, people disagree with calling something decentralized and trustless while funds are being frozen by centralized entities. Remove any mention of decentralization from the arbitrum website and docs. fair?

Reply with every tweet below that disagrees with Arbitrum freezing funds or citing pure decentralization. Then we’ll know which one of these anons are DPRK agents
👇
11
1
159


AAVE's moat of being the standard of safety/never been exploited "just use aave" is dead and it's a good thing.
The moat was undeserved, they almost got completely wiped out a few times and got lucky (and arrogant) until the kelp fiasco. They also got greedy with all the lst looping, hardcoded USDe hack etc.
That being said, I hope all depositors fully recover soon and aave itself too.
1
132
quick way to know if you were affected by vercel hack👀

Vercel has been hacked!
According to @acceleratooooor , here's how to triage:
1. Go to admin.google.com
2. Security → Access and data control → API controls → App access control → Manage Third-Party App Access
3. Search for client ID:
110671459871-30f1spbu0hptbs60cb4vsmv79i7bbvqj
if found → revoke / block
1
252